Incident Response
24/7 cyber incident support
Hacked? Account compromised? Suspicious activity in your Microsoft 365 environment? Attic Security is available 24/7 to help with forensic investigation, stopping the attack and full recovery.
How we respond
During a security incident, every minute counts. Our team follows a proven methodology for fast and thorough response.
Intake
Phone call to assess the situation and determine the right course of action.
Investigation
Initial investigation of up to 2 days. Using our platform and tools, we quickly determine what happened and stop the incident.
Reporting
Detailed report on how the breach occurred, what abuse took place and what remediation actions are still needed.
Prevention
Concrete recommendations and measures to prevent recurrence and structurally improve your security.
Specialised in Microsoft 365
Attic Security specialises in Microsoft 365 security, including conducting investigations following a security incident in the cloud service.
In most incidents, such as account takeover of an employee, we start with an initial investigation of up to 2 days. Thanks to our platform and tooling, we can quickly determine what happened and stop the incident.
When should you call?
Don't hesitate. The faster you act, the more damage we can prevent.
Account compromised
An employee can no longer log in, or you see unknown activity in a mailbox.
Ransomware attack
Files are encrypted, systems are unreachable or a ransom has been demanded.
CEO fraud / BEC
Fraudulent payments, fake emails from a compromised account or suspicious financial requests.
Data breach
Sensitive data may have been viewed, copied or leaked to external parties.
Phishing incident
Employees fell for a phishing attack and shared their credentials.
Suspicious activity
Unusual login attempts, mailbox rules you don't recognise or unexplained changes.
Do it yourself
You can always call us, and during an active incident that is the fastest route. If you want to look for yourself first, there are two ways in. One secures evidence, the other gives you a verdict.
Secure the evidence: the Triage Tool
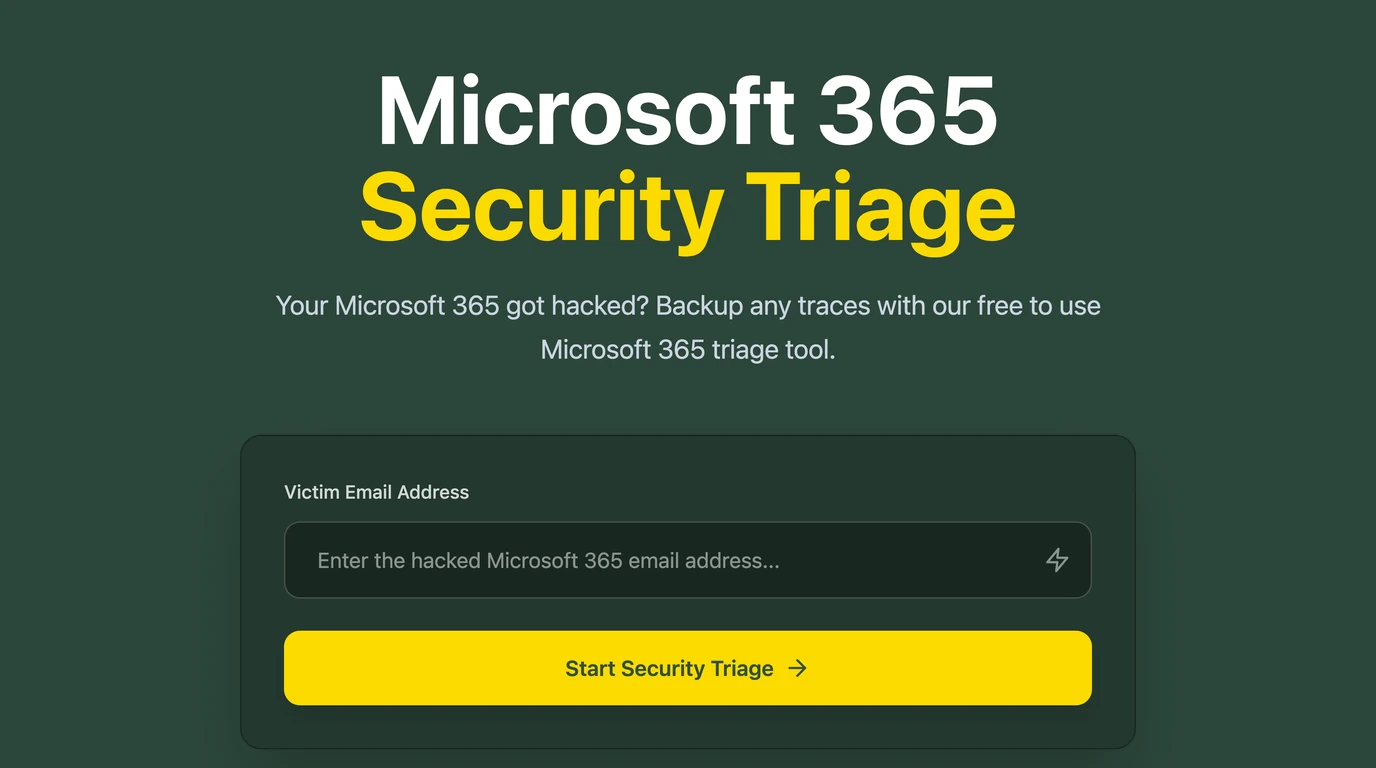
Microsoft 365 keeps log files for a limited time only. If you suspect an account has been taken over, pull the traces first. You enter the address of the suspected account, grant consent, and get a download link with the forensic log files. Attic then revokes the access it was granted.
- What you get
- An export, not a verdict. Ready for your own analysis, or for whoever runs the investigation.
Free, no account, no installation.
Get an extensive Incident Report from our AI SOC agent IVON within minutes
If there is an incident in your Microsoft Defender and you cannot tell how serious it is, put IVON on it. IVON follows the evidence trail and closes with a reasoned verdict. You watch along and download the report as a PDF.
Free, one incident per tenant. No installation.
The consent is delegated and read-only: nothing changes in your environment, and after twenty-four hours the data and the report are wiped.
Which of the two?
The Triage Tool collects evidence around one suspected account, even when Defender flagged nothing, and gives no verdict. The IVON incident investigation starts from an incident Defender has already raised and does give a verdict, but no raw export. If you are unsure, start with the Triage Tool. Evidence that is gone does not come back.
Why Attic for incident response?
Attic Security is not a generic IT company. We specialise in Microsoft 365 security and have built our own platform to analyse incidents at lightning speed. Our team has experience with hundreds of incidents and knows exactly where to look.
After the incident, we don't stop. We help your organisation become structurally more secure, so the same attack cannot succeed again.
Don't wait, call now
During a cyber incident, every minute counts. The sooner we're involved, the more damage we can prevent. Our team is available 24/7.